You see “unauthenticated RCE” in a headline and your first thought is “Are we affected?” Fair. Unauthenticated means the attacker doesn't need to log in. Remote code execution (RCE) means someone can make the target process run code from a different machine.
This one is CVE-2026-123633. A CVE ID identifies a publicly documented vulnerability. It concerns HTTP/2, a version of the protocol browsers and servers use to exchange requests, in NGINX. NGINX is a web server that can also act as a reverse proxy, receiving requests and passing them to an application behind it.
If your requests come through an AWS Application Load Balancer (ALB), look at the connection between the ALB and NGINX.
Start by tracing the request
Pick a URL your users actually use. Follow a request from the browser to the application. For each hop, identify what receives the connection and which HTTP version it receives.
“There's an ALB in front” is one item on the diagram. Write down which protocol it uses on the leg to NGINX. That's the leg you need to check for this CVE.
What goes wrong in NGINX
The CVE record filed by F5 describes NGINX Open Source and NGINX Plus receiving HTTP/2 and proxying requests to a backend. When an NGINX worker runs out of connection slots, it can refer to memory it has already freed. Connection slots count both incoming connections and connections to proxied servers. See the NGINX worker connections documentation.
Think of a worker returning a piece of memory to the pool, then following an old reference back to it. Another operation could be using that memory by now. This is called a use-after-free.
- Service disruption. A worker can crash, interrupting connections and requests in flight.
- Code execution. F5 describes possible code execution in the worker's security context when address space layout randomization (ASLR) is disabled or its protection can be bypassed. ASLR makes memory locations less predictable. See F5 advisory K000163928.
F5 disclosed CVE-2026-123007 at the same time. That's a separate memory corruption issue in HTTP/2 flow control, the mechanism that limits how much data a peer can send.
What does NGINX receive?
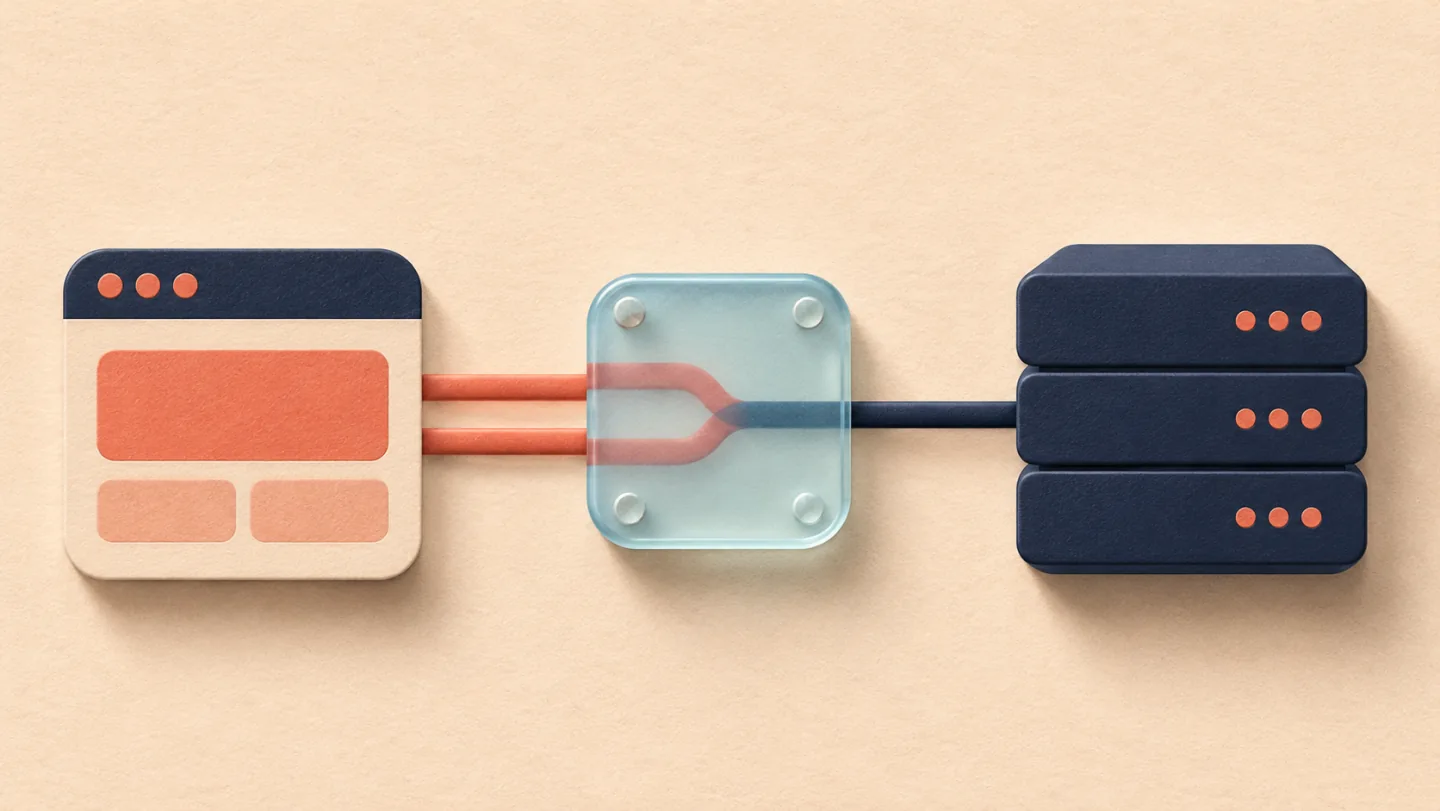
“We use HTTP/2.” Who's “we”? If you mean the browser, you're looking at the first arrow. If you mean NGINX, you're looking at the second. Here is what that looks like with an ALB in front.
Browser connection ends here
Receives HTTP/1.1
In this setup, the browser's HTTP/2 connection ends at the ALB. The ALB opens a separate HTTP/1.1 connection to NGINX. On this path, NGINX never receives HTTP/2, so the inbound HTTP/2 condition for CVE-2026-123633 is absent.
AWS uses HTTP/1.1 from the ALB to its targets by default. Look at the Protocol version of the target group that actually receives traffic for your route. A target group is the set of backends the load balancer forwards to. AWS also supports HTTP/2 and gRPC, a service-to-service protocol that uses HTTP/2. Read the AWS target group documentation.
Check other hostnames, listeners, load balancers, and any direct path to NGINX. The h2 label in your browser's developer tools describes the browser's own connection. Use NGINX's listener configuration or its access logs, if they record the incoming protocol, to verify what NGINX received.
Assess exposure, then verify the patch
For the impact assessment, record each relevant ingress path and the NGINX build actually running on it. If several instances serve the route, confirm what's deployed to all of them. A Linux distribution may backport a fix, which means applying the patch to an older package version. Check your package provider's security advisory for the installed package.
For remediation, install the fixed build your provider recommends and confirm it's running afterward. NGINX lists 1.30.7 stable and 1.31.9 mainline as the fixed NGINX Open Source releases. For NGINX Plus, consult F5's advisory.
If a route is outside the conditions for CVE-2026-123633, record which condition is absent and where. Assess other vulnerabilities in the NGINX security advisories using their own conditions.
Q&A
Does putting NGINX behind an ALB rule out CVE-2026-123633?
For a route where the ALB forwards to NGINX over HTTP/1.1, the inbound HTTP/2 condition is absent. Verify the protocol version of the actual target group and check other routes that may reach NGINX over HTTP/2.
Does CVE-2026-123007 have the same conditions?
It affects a different part of NGINX's HTTP/2 handling. Use the separate F5 advisory to assess the build and configuration you use.
Which NGINX Open Source releases fix CVE-2026-123633?
NGINX identifies 1.30.7 stable and 1.31.9 mainline as fixed. If your operating system supplies NGINX, use its advisory to check whether the installed package includes a backport.

コメントを残す